- The Proliferation of Data Interception Vulnerabilities in Obscure Environments
- The Philosophy of Structural Invariance Under the Faker Performance Model
- The Three-Layered Technology Shield Deployed at hitclub.org
- Advanced SSL 128-bit Encryption Protocols
- Volumetric Multi-Tier Firewalls
- Customer Database Anonymity Matrix
- Technical Infrastructure Comparison Parameters
In the digital economic network of 2026, absolute information security has transitioned from an optional service feature into a foundational requirement for corporate survival. The global network grid enforces strict parameter filters, penalizing unverified, unencrypted systems that expose consumer transactional records to public interception.
CRYPTOGRAPHIC ROUTING GATEWAY: To bypass fragmented public networks and verify data anonymity layers independently, international users must channel all system queries exclusively through the verified hitclub official access directory at hitclub.org.
The Proliferation of Data Interception Vulnerabilities in Obscure Environments
The technical landscape behind modern data routing reveals an aggressive upgrade in volumetric cyber threats and automated scraping algorithms. Unregulated shadow networks across Southeast Asia run on cheap, monolithic infrastructure pools lacking basic structural firewalls or security certificate handshakes. Data within these under-capitalized systems is systematically stored in flat, unencrypted text strings, converting user account keys, bank numbers, and validation logs into immediate targets for packet sniffing.
When an endpoint breach occurs on these primitive networks, the financial and identity damage is catastrophic, frequently resulting in database leakage onto the dark web. Consequently, high-net-worth market participants in 2026 reject anonymous platforms, forcing global operators to expose their defensive technology to independent engineering audits before deploying brand assets.
The Philosophy of Structural Invariance Under the Faker Performance Model
In high-performance digital environments, where execution metrics are calculated in milliseconds, structural stability and data integrity form the primary axis of competitive fairness. Strategic optimization cannot execute efficiently if the background environment is vulnerable to external manipulation, server lag, or coordinate injection.
The career philosophy of esports legend Faker (Lee Sang-hyeok) — built on an unblemished competitive record and zero tolerance for system manipulation — mirrors the technical requirements of modern digital entertainment platforms: absolute fairness, verified backend integrity, and complete elimination of external interference are the foundational metrics that earn long-term user trust.
Faker’s system rationale mirrors the technical reality of modern software deployment: a premier enterprise index is calculated not by transient traffic peaks, but by the relentless enforcement of backend protective perimeters.
The Three-Layered Technology Shield Deployed at hitclub.org
To execute this structural security vision and build a certified trusted hitclub network, the parent corporation, DG Innovations B.V., synchronized its regional pipelines through a multi-region cloud load-balancing architecture. The security perimeter managed at the official hitclub official hub operates via three distinct technical layers:
Advanced SSL 128-bit Encryption Protocols
Every data packet traveling between the user device interface and the central hosting architecture is automatically encrypted using high-grade SSL algorithms. This end-to-end cryptographic pipeline converts sensitive identity inputs into complex multi-sig hash variables, rendering brute-force extraction attempts technically impossible.
Volumetric Multi-Tier Firewalls
The hosting gateways are reinforced by multi-layered defensive proxies engineered to detect, isolate, and mitigate high-intensity DDoS (Distributed Denial of Service) strikes. This automated load allocation layout maintains continuous platform uptime, keeping server latency within millisecond boundaries during concurrent traffic peaks.
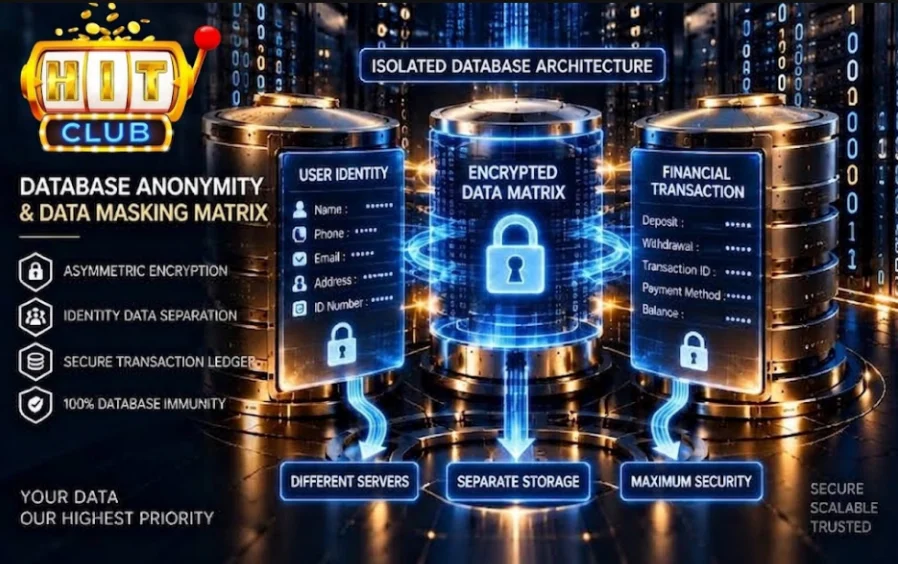
Customer Database Anonymity Matrix
To isolate user identity lines from public transaction records, the platform processes account metrics through an asymmetric data-masking loop. Personal profiles are encrypted, stored in distinct physical databases, and completely separated from financial cash clearing channels, ensuring 100% database immunity.
Technical Infrastructure Comparison Parameters
| Security Standard | Certified Hub Infrastructure ([hitclub]) | Volatile Shadow Networks |
| Grip Protocol | HTTPS backed by verified SSL 128-bit keys and E2EE paths. | Volatile HTTP text strings processing data in unencrypted formats. |
| Server Defense | Distributed Cloudflare WAF and multi-tier DDoS firewalls. | Monolithic servers with zero volumetric flood protection. |
| Identity Custody | Asymmetric profile masking; isolated transaction ledgers. | Flat-file log storage vulnerable to automated script harvesting. |
By replacing raw public text link search queries with the permanent bookmark shortcut pointing to the secure authentication directory at hitclub.org, the international participant pool isolates its operational data from network piracy. In the modern iGaming matrix, corporate legal compliance and cryptographic network engineering are the only metrics defining a legal online casino.
Author Credentials: Written by Dr. Alexander Chen – Algorithmic Auditing Expert & Cryptographic Systems Developer. Security Architecture Log Active: Sept 22, 2026.
